Send logs from A10 Networks vThunder application delivery controllers to Axoflow.
Vendors
Onboard vendor-specific source devices and hosts to Axoflow so they appear on the Topology page, send logs to AxoRouter, and report host metrics.
Prerequisites
- You have administrative access to the source device or host.
- You have an AxoRouter deployed and configured with a Syslog connector that has parsing and classification enabled (by default, every AxoRouter has such connectors). This device is going to receive the data from the source device or host.
-
You know the IP address the AxoRouter. To find it:
- Open the AxoConsole.
- Select the Routers or the Topology page.
- Select on AxoRouter instance that is going to receive the logs.
- Check the Networks > Address field.
Onboard a vendor source
To onboard sources that are specifically supported by Axoflow, complete the following steps. Onboarding allows you to collect metrics about the host, and display the host on the Topology page.
-
Open the AxoConsole.
-
Select Topology.
-
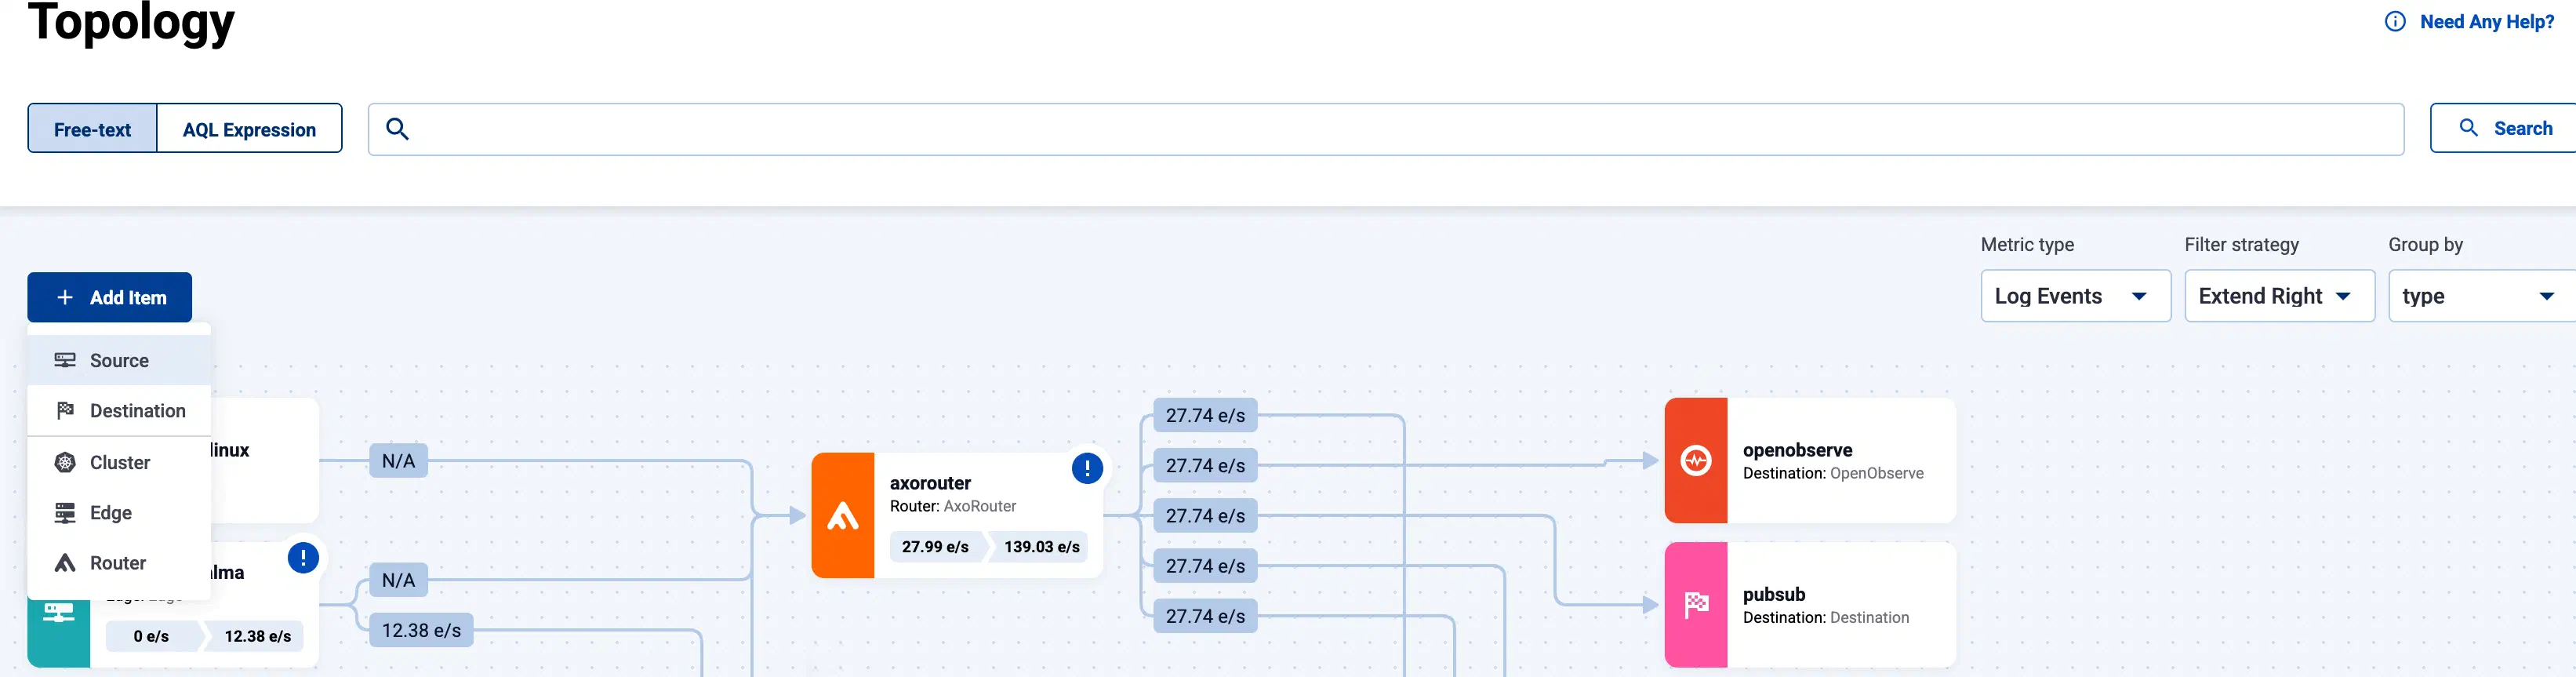
Select Add Item > Source.
-
Add the source to AxoConsole using one of the following methods:
-
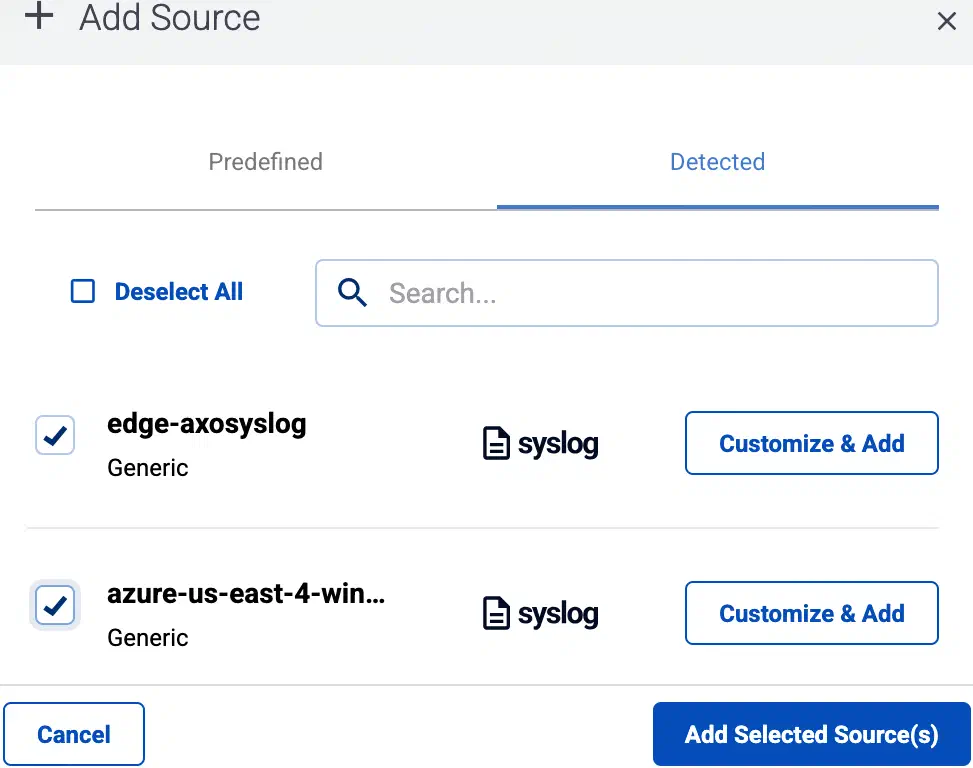
If the source is already sending logs to an AxoRouter instance that is registered in the AxoConsole, select Detected, then select the source.
You can add multiple detected sources in a single step in bulk.
-
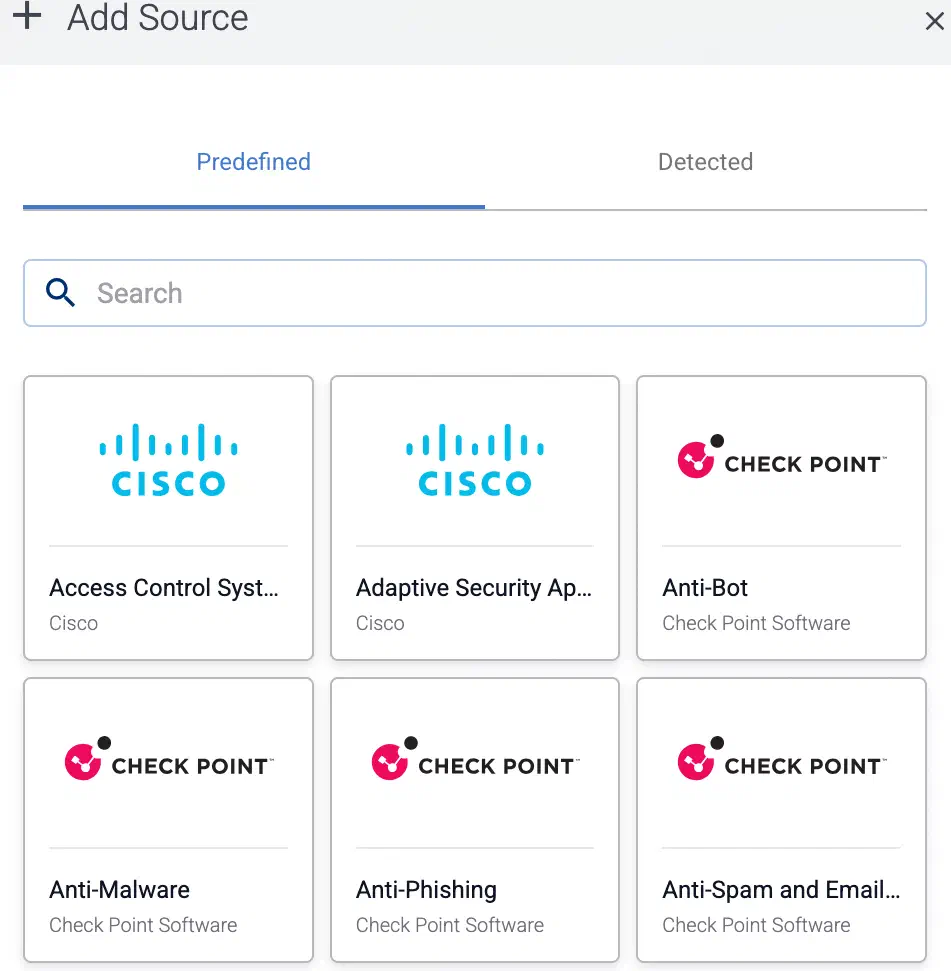
Otherwise, select the type of the source you want to onboard, and follow the on-screen instructions.
-
-
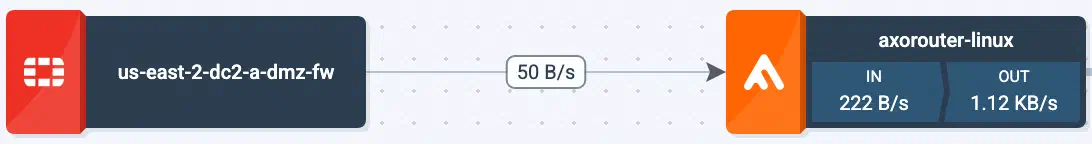
Connect the source to the destination or AxoRouter instance it’s sending logs to. If you’ve added the source from the Detected list, you can skip this step, as the path is created automatically.
-
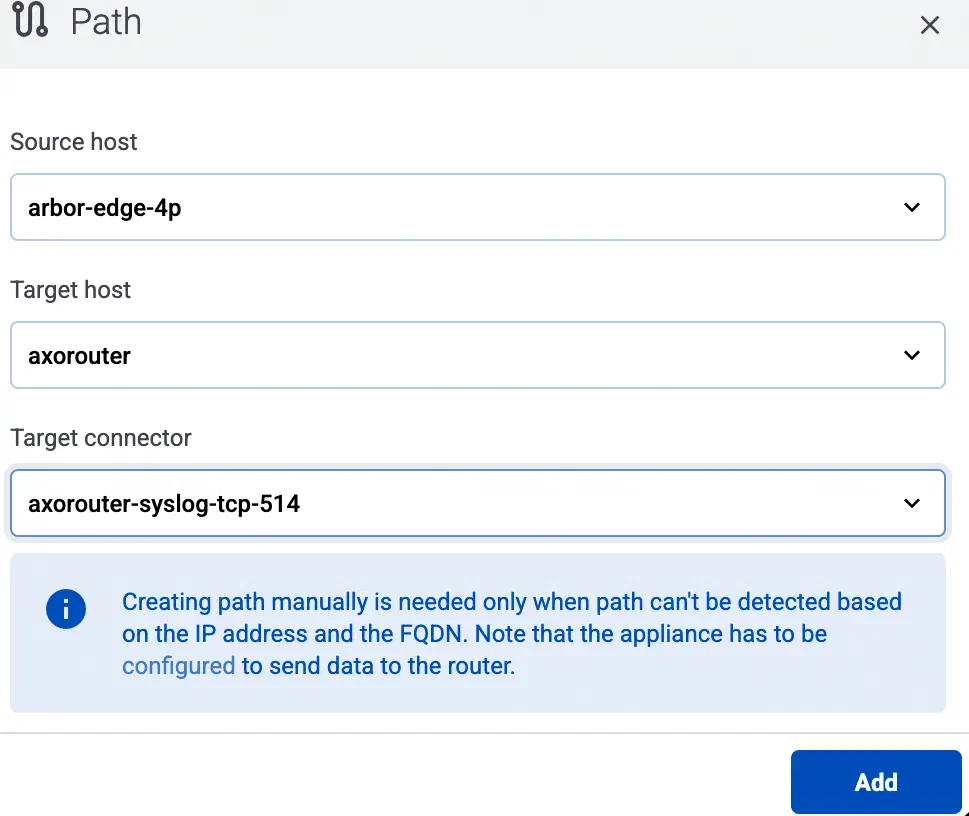
Select Topology > Add Item > Path.
-
If not set automatically, select the beginning of the path in the Source host field.
-
Select the target router or aggregator this source is sending its data to in the Target host field, for example,
axorouter. -
Select the Target connector. The connector determines how the destination receives the data (for example, using which protocol or port).
-
Select Add. The new path appears on the Topology page.
-
-
If you haven’t already done so, configure the source to send logs to an AxoRouter instance. For vendor-specific configuration steps, default metadata (labels), and SIEM-specific metadata, see the page for each source.
NoteUnless instructed otherwise, configure your source to send the logs to the Syslog connector of AxoRouter, using the appropriate port. Use RFC5424 if the source supports it.
- 514 UDP and TCP for RFC3164 (BSD-syslog) and RFC5424 (IETF-syslog) formatted traffic. AxoRouter automatically recognizes and handles both formats.
- 601 TCP (RFC 3195 - Reliable Delivery for syslog) for RFC5424 (IETF-syslog) and RFC3164 (BSD-syslog) formatted traffic. AxoRouter automatically recognizes and handles both formats.
- 6514 TCP for TLS-encrypted syslog traffic (RFC 5425).
A10 Networks
Amazon
Collect logs from Amazon CloudWatch and forward them to Axoflow for processing.
Axoflow
Send logs from your AxoSyslog instances to AxoRouter using the OpenTelemetry or syslog connector.
Broadcom
Send logs from Broadcom Edge SWG, Email Security, SSL Visibility Appliance, and VMware ESX, NSX, and vCenter to Axoflow.
Check Point
Send logs from Check Point Quantum, NGFW, IPS, SmartConsole, Threat Emulation, and other Check Point products to Axoflow.
Cisco
Send logs from Cisco ASA, Firepower, FTD, IOS, ISE, Meraki, and other Cisco devices to Axoflow.
Citrix
Send logs from Citrix NetScaler application delivery controllers to Axoflow.
Corelight
Forward logs from the Corelight Open Network Detection and Response (NDR) platform to Axoflow.
CrowdStrike
Collect security events from the CrowdStrike Falcon platform and send them to Axoflow.
CyberArk
Send logs from CyberArk Vault and Privileged Threat Analytics (PTA) to Axoflow.
F5 Networks
Send logs from F5 Networks BIG-IP application delivery appliances to Axoflow.
Forcepoint
Send logs from Forcepoint Next-Generation Firewall, Email Security, and WebProtect to Axoflow.
Fortinet
Send logs from Fortinet FortiGate firewalls, FortiMail, FortiProxy, and FortiWeb to Axoflow.
Fortra
Forward IBM i security events from the Fortra Powertech SIEM Agent to Axoflow.
General Unix/Linux host
Collect logs from common, non-vendor-specific services running on generic Unix and Linux hosts.
Imperva
Send logs from Imperva Incapsula and SecureSphere to Axoflow.
Infoblox
Send DNS, DHCP, and IPAM logs from Infoblox NIOS to Axoflow.
Ivanti
Send logs from Ivanti Connect Secure VPN appliances to Axoflow.
Juniper
Send logs from Juniper routers, switches, and firewalls running Junos OS to Axoflow.
Kaspersky
Send logs from Kaspersky Endpoint Security to Axoflow for processing and routing.
Kubernetes
Collect logs from Kubernetes clusters, including NGINX Ingress, with Telemetry Controller and send them to Axoflow.
Microsoft
Collect data from Windows hosts, Azure Event Hubs, and Microsoft Cloud App Security (MCAS) with Axoflow.
MikroTik
Send logs from MikroTik routers running RouterOS to Axoflow.
NetFlow Logic
Send flow data processed by NetFlow Logic NetFlow Optimizer to Axoflow.
Netgate
Send firewall logs from Netgate pfSense appliances to Axoflow.
Netmotion
Send logs from Netmotion to Axoflow and see which labels Axoflow adds to them.
NETSCOUT
Send logs from NETSCOUT Arbor Edge Defense (AED) and Arbor Pravail (APS) to Axoflow.
Omnissa
Send logs from Omnissa Horizon (formerly VMware Horizon) to Axoflow.
OpenText
Send logs from OpenText ArcSight and Self Service Password Reset (SSPR) to Axoflow.
Palo Alto Networks
Send logs from Palo Alto Networks firewalls running PAN-OS and from Cortex XSOAR to Axoflow.
Ping Identity
Collect logs from Ping Identity PingAccess and send them to Axoflow.
Progress
Send logs from the Progress Flowmon Anomaly Detection System (ADS) to Axoflow.
Riverbed
Send logs from Riverbed SteelHead and SteelConnect appliances to Axoflow.
RSA
Send authentication logs from RSA Authentication Manager to Axoflow.
SecureAuth
Collect logs from the SecureAuth Identity Platform and send them to Axoflow.
Skyhigh Security
Send logs from the Skyhigh Security Secure Web Gateway to Axoflow.
SonicWall
Send firewall and VPN logs from SonicWall appliances to Axoflow.
Splunk
Route data from Splunk Universal Forwarders and Heavy Forwarders into Axoflow.
Superna
Send logs from Superna Eyeglass to Axoflow for processing and routing.
Tanium
Collect data from the Tanium Platform and forward it to Axoflow for processing.
Thales
Send logs from the Thales Vormetric Data Security Platform to Axoflow.
Trellix
Send logs from Trellix ePO, Endpoint Security (HX), Email Threat Prevention, IPS, CMS, and MPS to Axoflow.
Trend Micro
Collect logs from Trend Micro Deep Security Agent and send them to Axoflow.
Ubiquiti
Send logs from Ubiquiti UniFi network devices to Axoflow for processing.
Varonis
Send logs from Varonis DatAdvantage to Axoflow for processing and routing.
Vectra AI
Send detections from the Vectra AI Platform (formerly Vectra Cognito) to Axoflow.
Zscaler appliances
Send logs from Zscaler Nanolog Streaming Service (ZIA) and Log Streaming Service (ZPA) to Axoflow.