Access management
Axoflow users can have different levels of access to AxoConsole based on their roles.
Authorization can be based on group memberships, email domains, and individual email addresses.
Roles
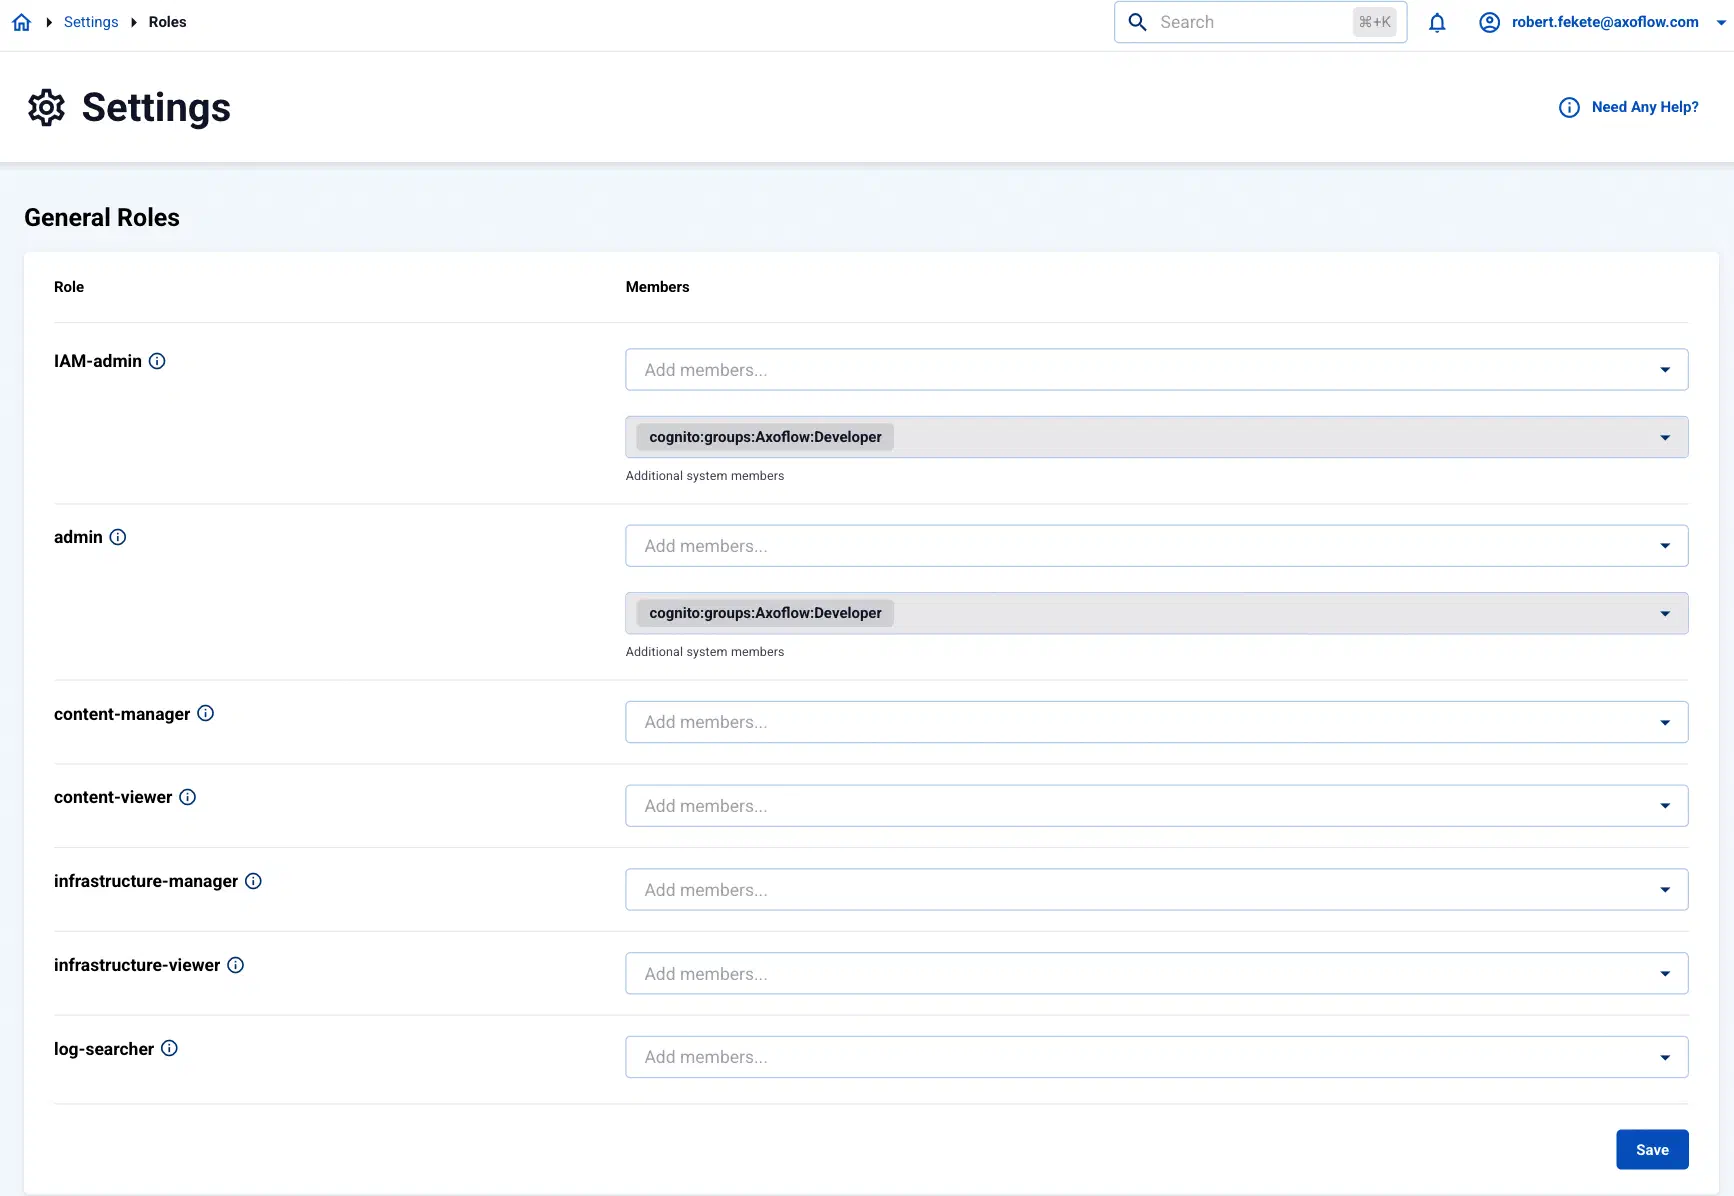
The following roles are available in AxoConsole by default:
-
IAM-admin: Can manage the roles and permissions to access AxoConsole. Only this role can make changes on the Settings > Roles page. If your identity provider has an administration page, this role can also see the Identity Provider Admin Panel link to it on the Settings > Roles page. (If your identity provider has a profile page, every user can open their own profile by selecting <their username> > Profile in the top-right corner.)
-
admin: Has full access to AxoConsole, except:
- Has only read access to the Settings > Roles page.
- Can’t search logs in stores. Searching requires the log-searcher role, or an access role to the specific store.
-
infrastructure-manager: Can manage the infrastructure (without the permissions to view or tap log contents, or to rehydrate data). Has full access to the following pages: Activity Logs, Alerting, Routers, Sources, Flows, Provisioning, Search Logs. Can tap into service logs which may contain event payload.
-
infrastructure-viewer: Similar to infrastructure-manager, but can only view the pages.
-
content-manager: Can view log content and manage content related details like flows (without the permissions to manage infrastructure, but including access to view infrastructure details).
- Has full access to the Rehydration page.
- Can view and modify Flows, but can’t create or delete them.
- Can view Routers, Sources, Search Logs, Analytics.
- Can tap into logs.
-
content-viewer: Can view content like analytics, log search, log tapping (without the permissions to manage or view infrastructure details).
- Can view Search Logs, Analytics.
- Can tap into logs.
-
log-searcher: Can search in every store. You can also grant access to specific stores.
If you need other roles, contact the Axoflow support team . Composing other roles is possible as part of a custom integration.
Manage access
To add new members to a role, complete the following steps. You need the IAM-admin role to manage the roles.
-
Navigate to Settings > Roles.
-
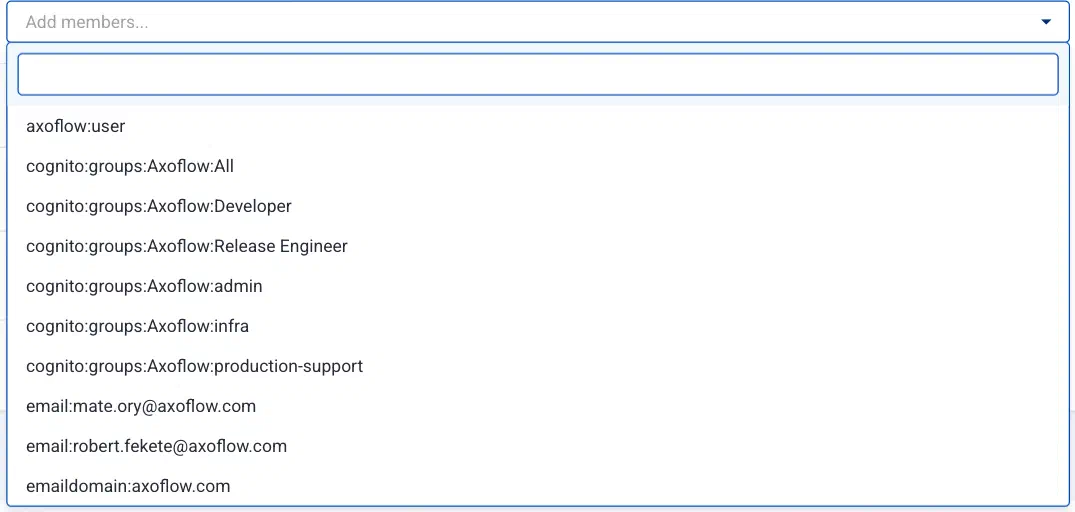
In the General Roles list, select the Add members… field of the role, and select or type the member. You can add:
-
A specific email address, for example,
email:username@example.comNote- The user must be able to authenticate to AxoConsole using this email address, so authentication must be properly set up.
- Multiple identity providers may allow authentication with the same email address, possibly with different level of ownership validation.
-
An entire email domain, for example,
emaildomain:example.com. Any user who authenticates with an email address belonging to this email domain will have access to the role. -
A user group. The format of the group depends on the OID provider.
- If you’re using AxoConsole as a SaaS, specify the group in the following format:
cognito:groups:<groupname-retrieved-from-cognito>, for example,cognito:groups:ExampleGoogleSaml:Operator. - If you’re using an on-prem AxoConsole deployment, specify the group in the following format:
groups:<groupname-retrieved-from-dex>for example,groups:operator.
- If you’re using AxoConsole as a SaaS, specify the group in the following format:
-
A specific session of an authenticated user, in the following format:
user:<oidc-response-subject>, for example:user:42c4e962-f077-705f-138f-f01ba1220c44. -
Every authenticated user:
axoflow:user
-
-
Select Save.
Some members are fixed: the Additional system members field of the role lists them, and you can’t remove them. They were added during the integration at the request of your organization, or during the initial configuration of on-premises deployments.
Store access roles
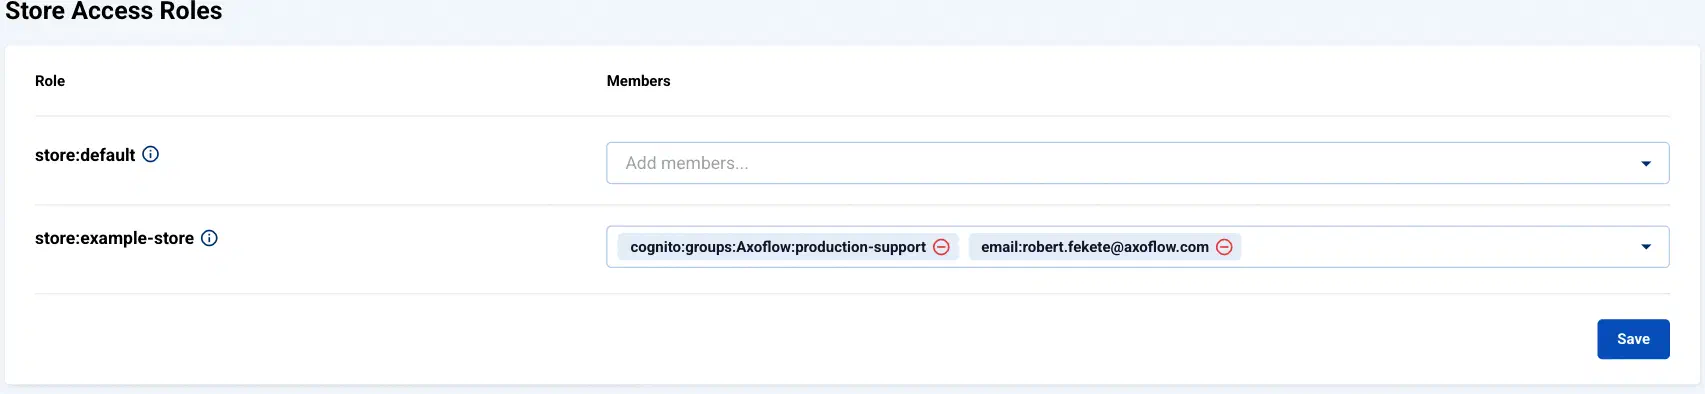
The Store Access Roles grant search access to a specific store. The Store Access Roles section of the Settings > Roles page lists every configured store. To grant search access to a specific store, add the group or user to the Members of the store, then select Save in the Store Access Roles section. To grant access to every store, use the log-searcher role instead.
CAUTION:
These access roles have effect only when the user searches the store using AxoConsole. It doesn’t have any effect if someone gains direct access to the store files (for example, when accessing the stores on an AxoRouter from a terminal).